Cron - The Banking Trojan


Couple of days ago, the world's cyber crime media has announced the arrest of Cron. This "little" gang -

Every day Cron malware attempted to steal money from 50-60 clients of different banks. The gang's infection vector included spam SMS messages and fake applications.


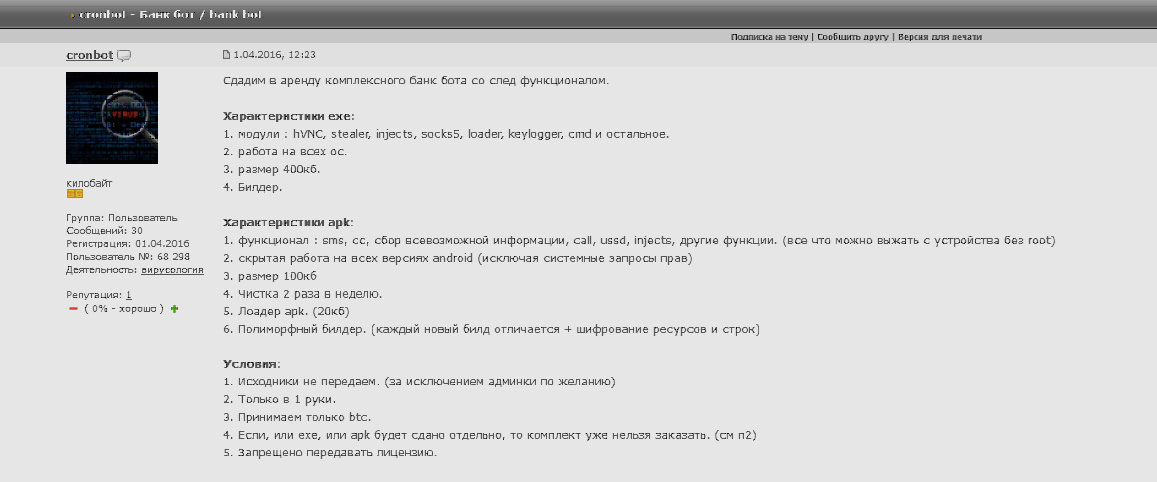
In April 2016, an announcement about the lease of a mobile Trojan called cronbot appeared on a famous hacker forum (http://exploit.in). According to its description, the Trojan had the functionality to intercept SMS messages and calls, send USSD requests, and perform web injections. Group-IB assumed that the criminal group decided to recruit a new member to the team, because according to the author of the announcement, they were ready to provide the Trojan to one person only. At the time, the group consisted of the organizers, operators, "cryptors", "traffickers" and money mules.


Cron planned to start their "international activity" with attacks targeting banks of France. They developed special web injections for the following French financial institutions: Credit Agricole, Assurance Banque, Banque Populaire, BNP Paribas, Boursorama, Caisse d'Epargne, Societe Generale and LCL.

However, by November 2016, Russian legal enforcement with support from Group-IB had managed to identify all members of the group and collect digital evidence of the crimes committed. On November 22, 2016, a large-scale operation was carried out in 6 Russian regions: 16 Cron members were detained. The last active member of the group was detained in early April in St. Petersburg.


Comments

Popular posts from this blog

Czech Republic announced it had extradited the Russian hacker Yevgeni Nikulin (29) to the United States

Yevgeni Nikulin (29) was requested by the US for alleged cyber attacks on social networks and by the Russian authorities that charged him with frauds. According to US authorities, the man targeted LinkedIn and Formspring and hacked into the file hosting service Dropbox. The Russian criminal was arrested in Prague in October 2016 in an international joint operation with the FBI. The case in the middle of an arm wrestling between Moscow and Washington, the US Government are accusing Russia to have interfered with 2016 Presidential election  through hacking . Source: US Defense Watch.com In May, a Czech court ruled that Nikulin can be extradited to either Russia or the United States, leaving the final decision to the Justice Minister Robert Pelikan. “It is true there have been two meetings this year where the president asked me not to extradite a Russian citizen to the United States but to Russia,” the website of the weekly newspaper Res...

‘Infraud’ Cybercrime Forum is Busted, 13 hackers arrested & 36 charged

The U.S. Justice Department announced charges on Wednesday against three dozen individuals thought to be key members of ‘ Infraud ,” a long-running cybercrime forum that federal prosecutors say cost consumers more than a half billion dollars. In conjunction with the forum takedown, 13 alleged Infraud members from the United States and six other countries were arrested. Started in October 2010, Infraud was short for “In Fraud We Trust,” and collectively the forum referred to itself as the “Ministry of Fraudulently [sic] Affairs.” As a mostly English-language fraud forum, Infraud attracted nearly 11,000 members from around the globe who sold, traded and bought everything from stolen identities and credit card accounts to ATM skimmers, botnet hosting and malicious software. “Today’s indictment and arrests mark one of the largest cyberfraud enterprise prosecutions ever undertaken by the Department of Justice,” said John P. Cronan , acting assistant attorne...

NiceHash: security breach leads to 60 million lost - Iceman is behind?

A dark day for crypto currency miners, NiceHash has been hacked. Closely to 60$ millions (4,736.42 BTC) have been stolen while the bitcoin is crossing the 14k$ mark for the first time. The hacker's bitcoin address cleary shows the steal of  4,736.42 BTC in a window of 48 hours: https://bitinfocharts.com/bitcoin/address/1EnJHhq8Jq8vDuZA5ahVh6H4t6jh1mB4rq NiceHash users are furious by the time of reaction of the team. It took about 24 hours to realise that big amounts have been stolen. I've contacted a member of Iceman and knowing this security breach for some reason he explained that NiceHash actually owned their users bitcoin wallets in order to save transactions fees and collect unclaimed BTC. This issue leads to a massive security breach which allow access to all NiceHash wallets. He claimed that by reverse engineering of their miner client, Iceman group was able to access their API. Is Iceman really behind this attack?